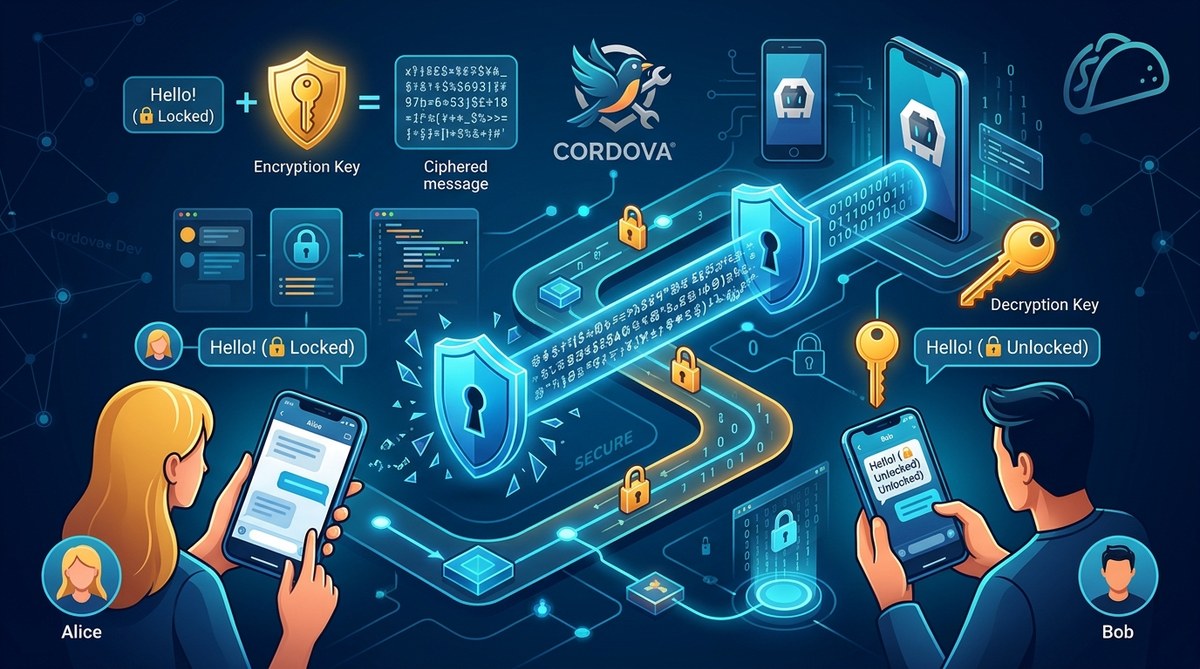
If you are building a chat app with Apache Cordova, you already know the challenge of balancing cross-platform reach with user trust. Nothing builds trust like knowing a message is truly private. End-to-end encryption (E2EE) ensures that only the sender and recipient can read a message. Not your server, not an ISP, not even the platform itself. For a Cordova app, this means adding a layer of security that works on both Android and iOS without rewriting your entire codebase. Let’s walk through how to make that happen.
Implementing end-to-end encryption in your Cordova chat app boils down to three steps: picking a proven cryptographic library like the Signal Protocol, managing key exchange securely on each device, and integrating it into your message flow. This guide gives you the practical process, common pitfalls, and a clear path forward for 2026.
Why Cordova needs a special approach to E2EE
Apache Cordova apps run inside a WebView. They are essentially web applications packaged as native mobile apps. This means your JavaScript code runs in a sandboxed environment. You cannot directly access the device’s secure hardware (like a TPM or Secure Enclave) without a plugin. That limitation makes E2EE implementation a bit different compared to a fully native app.
Your cryptographic operations must happen in the JavaScript layer or via a native plugin bridge. The good news? Several libraries are designed to work in this exact scenario. The key is to keep private keys on the device and never send them to your server.
Choosing the right encryption library for your Cordova app
You need a library that supports the Signal Protocol (the gold standard for messaging apps like WhatsApp and Signal). Here are the top options for a Cordova environment:
- libsignal-client: The official Signal library. It is written in Rust and compiled to native code. You will need a Cordova plugin to call it from JavaScript.
- Signal Protocol JavaScript (signal-protocol): A pure JavaScript implementation. Slower than native, but easier to integrate. Good for smaller user bases.
- OpenPGP.js: For a different encryption model (asymmetric key pairs). Not ideal for real-time chat, but useful for file encryption.
For most Cordova chat apps, the pure JavaScript Signal Protocol library is the best starting point. It avoids the complexity of compiling native code for multiple platforms.
Step-by-step: Integrating E2EE into your Cordova chat app
Let’s break this down into a numbered process. These steps assume you have a basic Cordova project with a chat interface already working.
1. Install the Signal Protocol library
Add the library to your project using npm. Open your terminal in the project root.
npm install signal-protocol
This library handles the cryptographic primitives: key generation, message encryption, and message decryption. It does not handle network transport. That part is still your job.
2. Generate identity keys and prekeys
When a user registers or logs in for the first time, you need to generate a set of keys. These keys live on the device and never leave it unencrypted.
const signal = require('signal-protocol');
const identityKeyPair = signal.KeyHelper.generateIdentityKeyPair();
const signedPreKey = signal.KeyHelper.generateSignedPreKey(identityKeyPair, 0);
const preKeys = signal.KeyHelper.generatePreKeys(0, 100);
Store the private part of the identity key in a secure location on the device. For Cordova, you can use the cordova-plugin-secure-storage or encrypt it with a user PIN before saving to local storage.
3. Register public keys with your server
Your server needs the public parts of these keys so other users can look them up. Send the public identity key, the signed prekey, and a batch of one-time prekeys to your backend.
- The server stores these keys and deletes a one-time prekey after it is used.
- Never send the private keys to the server. If you do, you have broken the “end-to-end” promise.
4. Build a session when two users start chatting
When User A wants to message User B, they fetch User B’s public keys from the server. Then they build an encrypted session.
const sessionBuilder = new signal.SessionBuilder(store, address);
const session = sessionBuilder.processPreKeyBundle(bundle);
This session object contains the shared secret. Both users now have a common encryption key without ever sharing it over the network.
5. Encrypt and decrypt messages
Now you can wrap your message sending logic. Before sending a message, encrypt it with the session.
const ciphertext = signal.SessionCipher.encrypt(session, plaintext);
// ciphertext is a JSON object with type and body fields
Send the ciphertext object to your server. The server forwards it to the recipient. On the receiving end, the Cordova app uses its local session to decrypt.
const plaintext = signal.SessionCipher.decrypt(session, ciphertext);
That is the core loop. Each message is encrypted on the sender’s device and decrypted on the recipient’s device. Your server never sees the plaintext.
Common mistakes when adding E2EE to a Cordova app
Here is a table of the most frequent errors developers make, along with how to avoid them.
| Mistake | Why it hurts | How to fix it |
|---|---|---|
| Storing private keys in plain text in local storage | Anyone with device access can steal keys | Use a plugin like cordova-plugin-secure-storage or derive keys from a user passphrase |
| Sending private keys to the server for “backup” | Breaks the end-to-end guarantee entirely | Never transmit private keys. Offer users a recovery phrase instead |
| Using the same prekey bundle for all devices | Breaks forward secrecy | Generate unique prekeys per device and rotate them regularly |
| Ignoring message ordering | Decryption fails if messages arrive out of order | Include a message counter in the ciphertext and handle reordering on the client |
| Not handling session expiration | Old sessions can be replayed | Set a session expiration time and force a new key exchange after that period |
Blockquote: “The most common security flaw I see in Cordova chat apps is not the encryption algorithm itself, but how developers manage the keys. If your private key is stored in a file that any other app can read, the strongest encryption in the world won’t protect your users.” — Sarah Chen, mobile security engineer
What about group chats?
Group E2EE is more complex. Each message must be encrypted once and then decrypted by every member. The Signal Protocol handles this with a “sender key” that is shared among group members. For a Cordova app, you can use the same signal-protocol library. The process is similar, but you need to manage a group session object in addition to individual sessions.
- Each group member generates a sender key.
- The sender key is encrypted with each member’s individual session key and sent out.
- Once everyone has the sender key, messages are encrypted with that key.
Group E2EE adds overhead, especially when members join or leave. You must rotate the sender key on membership changes to prevent former members from reading new messages.
Testing your E2EE implementation
You cannot ship an encryption feature without testing it thoroughly. Here is what you should verify:
- Key generation: Run the key generation code on multiple Android and iOS versions. Ensure it does not crash.
- Session creation: Simulate two devices exchanging keys through a test server. Confirm the session is established.
- Message round trip: Send a message from device A to device B. Decrypt on B. Compare the plaintext.
- Tamper detection: Modify a ciphertext in transit. The decryption should fail gracefully, not crash the app.
- Prekey exhaustion: Use up all one-time prekeys and verify the session still works (it should fall back to a new key exchange).
For more tips on debugging your app, check out our guide on essential debugging tips for hybrid Cordova applications.
Tools and plugins that make E2EE easier in Cordova
You do not have to build everything from scratch. These plugins and libraries can accelerate your development:
- cordova-plugin-secure-storage: Stores sensitive data in the device’s secure area (Keychain on iOS, KeyStore on Android).
- signal-protocol: The JavaScript library we used above.
- libsodium.js: A JavaScript port of the popular NaCl library. Useful if you want a different cryptographic foundation.
- Web Crypto API: Cordova supports the browser’s built-in crypto API. You can use it for hashing and random number generation.
If you are looking for more ways to speed up your workflow, see our list of top tools and plugins to accelerate Cordova app development.
Migrating an existing chat app to E2EE
If you already have a chat app running without encryption, you cannot just flip a switch. Old messages are already in plaintext on your server. Here is a practical migration path:
- Add E2EE as an optional feature first. New messages are encrypted. Old messages remain readable.
- Give users a way to delete old message history if they want full privacy.
- After a transition period (30 to 90 days), make E2EE the default.
- Eventually, remove the fallback for plaintext messages.
This approach prevents breaking the app for existing users while moving toward a fully encrypted system.
Securing the whole app, not just messages
E2EE protects messages in transit and at rest on the server. But your app still has other attack surfaces. A malicious plugin or a compromised dependency could read the plaintext before it is encrypted. Follow these best practices:
- Audit your Cordova plugins regularly. Remove any that you do not need.
- Keep your dependencies updated. An outdated library might have a known vulnerability.
- Use a Content Security Policy (CSP) to prevent XSS attacks that could steal keys.
- Consider implementing biometric authentication for an extra layer of device security. Our guide on how to implement biometric authentication in your Cordova app for 2026 covers this.
Your next steps for a secure Cordova chat app
Adding end-to-end encryption to your Cordova chat app is a significant engineering effort, but it is one of the best investments you can make in user trust. Start with the Signal Protocol library, manage keys carefully on the device, and test every edge case. Do not try to invent your own cryptography. Use proven standards.
The payoff is a chat app that users can trust with their most sensitive conversations. That trust translates into retention and word-of-mouth growth. And in 2026, privacy is not a nice-to-have. It is a baseline expectation.