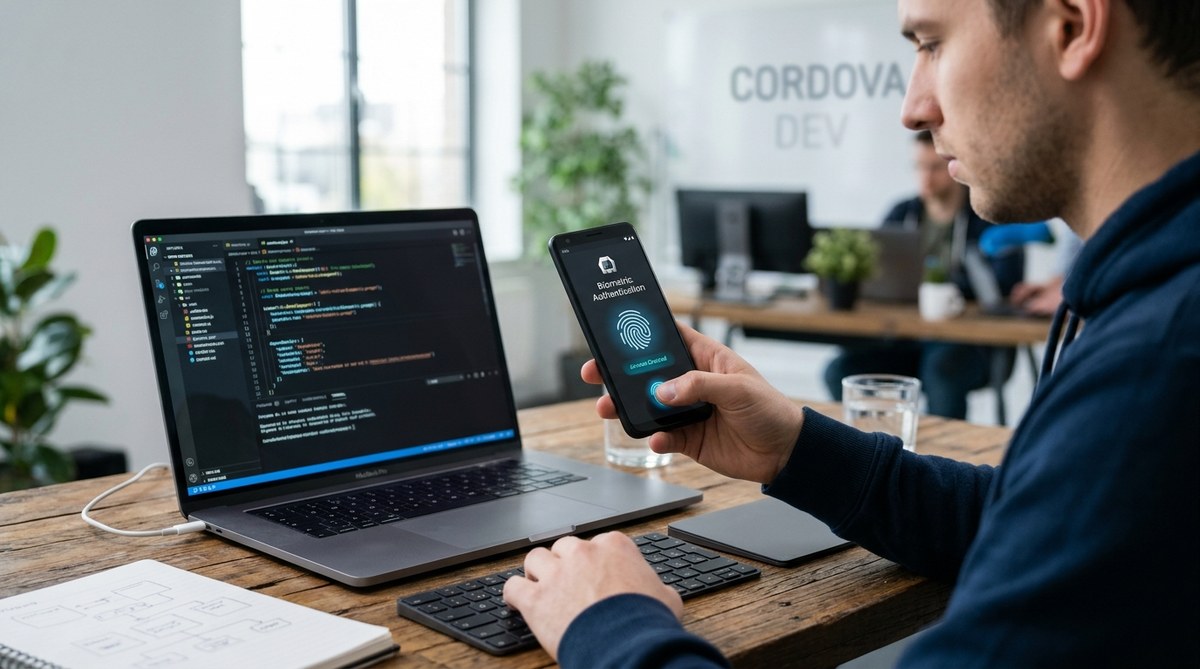
Fingerprint login and face unlock used to feel like sci-fi. Now they are the default expectation for any mobile app that handles sensitive data. If you are building with Cordova, the good news is that you do not need to rewrite your app in Swift or Kotlin to offer this. You can bridge the gap between your JavaScript code and the device’s native biometric hardware using plugins, native SDKs, and a little bit of platform-specific wiring.
Adding biometric authentication to a Cordova app in 2026 requires a hybrid approach. Use Cordova plugins like cordova-plugin-fingerprint or cordova-plugin-face-camera for basic capture, then pass the raw biometric data to a native SDK on each platform. iOS uses Apple’s WebAuthn APIs via the iOS Biometric SDK, while Android relies on the Android Biometric API. Server-side verification handles the rest. This guide walks through the exact steps.
Why Cordova Developers Need a Different Approach
Pure JavaScript apps cannot access the phone’s fingerprint sensor or infrared camera directly. The WebView layer that Cordova wraps around your HTML and CSS does not expose those hardware channels. You need a bridge. That bridge is either a custom Cordova plugin or a platform-specific native SDK that you call through a plugin wrapper.
The challenge is that biometric hardware varies wildly between devices. An iPhone 16 has a different fingerprint sensor than a Samsung Galaxy S26. Your Cordova app must handle both without breaking the user experience.
The Three Main Integration Paths for 2026
You have three realistic options for cordova biometric authentication implementation. Each comes with tradeoffs in complexity, security, and user experience.
Option 1: Cordova Plugin Wrappers
Several community plugins wrap native biometric APIs. These are the fastest path to a working prototype. The plugin handles the JavaScript-to-native bridge so you can call a fingerprint.capture() function from your app code.
Popular plugins include:
– cordova-plugin-fingerprint (Android and iOS)
– cordova-plugin-face-camera (iOS only)
– cordova-biometric-auth (cross-platform but requires API key)
These plugins work well for basic fingerprint scanning and face capture. They hand you a base64-encoded image or a raw template that you then send to your authentication server.
Option 2: Native SDK via Custom Plugin
For production apps, you will want tighter control. Write a small Cordova plugin that calls the platform’s native SDK directly. On iOS, that means Apple’s WebAuthn and Biometric APIs. On Android, you use the Android Biometric API or the hardware SDK from the phone manufacturer.
This path requires some C++ or Java code, but it gives you access to liveness detection and encryption that the community plugins skip.
Option 3: Server-Side Biometric Verification
The most secure approach keeps the biometric template on the device and only sends a cryptographic challenge to your server. This prevents a data breach from exposing actual fingerprints or face scans. Services like Apple’s iCloud Keychain and Android’s Titan Security use this model.
Your Cordova app captures the biometric, encrypts it locally, and sends only a signed hash to your backend for verification.
Step-by-Step Implementation
Let’s walk through a real implementation using a custom Cordova plugin that wraps the iOS and Android biometric SDKs.
Step 1: Set Up Your Cordova Project
Start with a clean project and add the required plugin scaffolding.
cordova create my-secure-app
cd my-secure-app
cordova plugin add cordova-plugin-biometric-auth
If you are building your own plugin, use the cordova plugin create command and structure it with separate folders for src/android and src/ios.
Step 2: Configure Platform Permissions
Biometric access requires explicit user permission. On iOS, you need to add a capability to your manifest.json. On Android, you request BIOMETRIC_PERMISSION at runtime.
For iOS, add this to your app.config:
{
  "capabilities": [
    "biometric"
  ]
}
On Android, your plugin’s Java code should call:
biometricManager.requestPermission(
  BiometricPermission.FINGERPRINT,
  "Use your fingerprint to sign in"
);
Step 3: Capture the Biometric
In your JavaScript, call the capture method:
function captureFingerprint() {
  window.plugins.biometricAuth.capture({
    type: 'fingerprint',
    timeout: 30,
    livenessCheck: true
  }, function(success, data) {
    if (success) {
      // data.template contains the encrypted biometric
      sendToServer(data.template);
    } else {
      showError('Could not capture fingerprint. Try again.');
    }
  });
}
The livenessCheck parameter is critical. It tells the sensor to check for a real finger versus a silicone print. Most modern phones support this at the hardware level.
Step 4: Verify on the Server
Send the template to your authentication server. The server compares it against the stored template for that user. Never store raw images. Store only the mathematical representation of the fingerprint or face.
function sendToServer(template) {
  fetch('/api/auth/biometric', {
    method: 'POST',
    headers: { 'Content-Type': 'application/json' },
    body: JSON.stringify({ userId: currentUser.id, template: template })
  }).then(response => response.json())
    .then(result => {
      if (result.authenticated) {
        navigateToDashboard();
      } else {
        showError('Biometric did not match. Try your password.');
      }
    });
}
Common Mistakes and How to Avoid Them
Here is a table of the most frequent pitfalls developers run into during cordova biometric authentication implementation.
| Mistake | Why It Hurts | Fix |
|---|---|---|
| Storing raw biometric images on the server | A breach exposes irreversible biometric data. | Store only hashed templates. Use salted SHA-256. |
| Skipping liveness detection | Attackers can use photos or prints to spoof the sensor. | Always enable liveness checks on both platforms. |
| Hardcoding API keys in the Cordova app | Anyone who decompiles your app can steal the key. | Use a backend proxy or PKCE flow for authentication. |
| Ignoring platform-specific permission dialogs | iOS and Android reject the request silently. | Test on real hardware, not just emulators. |
| Using the same template format for both iOS and Android | The raw data structures differ. | Normalize at the server level before comparison. |
Security Considerations That Matter
“Biometric data is not a password. You cannot change your fingerprint when it gets stolen. Treat it like a permanent identifier and encrypt everything.” – OWASP Mobile Security Guide
Your Cordova app must never transmit raw biometric data over HTTP. Use TLS 1.3 at minimum. Encrypt the template on the device before sending it. On iOS, the Secure Enclave handles this. On Android, the TPM (Trusted Platform Module) does the same.
You also need a fallback for users whose biometric sensors fail. Cold fingers, wet hands, and dirty camera lenses all cause false rejections. Always offer a PIN or password as a backup.
A Practical Workflow for Your Team
Follow this numbered process to roll out biometric auth without breaking your existing login flow.
- Add the biometric plugin to your Cordova project and test the capture method on a physical device.
- Implement server-side template storage with a separate database table for biometric hashes.
- Add liveness detection and test with photos, videos, and silicone prints to confirm rejection.
- Build a fallback login screen that appears when the biometric sensor fails three times.
- Run a security audit on the data flow from sensor to server.
- Ship a beta to a small group of users and monitor false rejection rates.
- Tune the sensor sensitivity based on real-world feedback before full release.
What to Test Before Launch
- Test on older devices. An iPhone 12 handles biometrics differently than an iPhone 16.
- Test in low light if you use facial recognition.
- Test with wet and dry fingers for fingerprint sensors.
- Test the fallback flow by disabling the sensor in the device settings.
For more on debugging these edge cases, check out our guide on essential debugging tips for hybrid Cordova applications.
Keeping Your Biometric Implementation Maintainable
Biometric SDKs change every year. Apple and Android both update their APIs with major OS releases. You need a maintenance plan.
- Abstract the biometric logic behind a single JavaScript interface. If the iOS SDK changes, you only update the iOS plugin code.
- Use feature flags to disable biometric auth on devices that do not support it.
- Monitor your error logs for
BIOMETRIC_NOT_AVAILABLEerrors and route those users to password login automatically.
For a deeper look at plugin architecture, read mastering Cordova plugin development for cross-platform compatibility.
Getting the Green Light from Your Security Team
Security teams often push back on biometrics because of data retention laws and breach risks. Address their concerns upfront by showing that your implementation never stores raw images and uses device-side encryption. Share the OWASP guidelines and demonstrate the fallback flow.
If your app handles financial data or health records, you may need SOC 2 compliance for your biometric server. Plan for that in your architecture.
The Developer Experience You Should Aim For
A well-implemented biometric login should feel invisible. The user opens your app, places their finger on the sensor, and lands on the dashboard. No typing. No waiting for SMS codes. That is the standard in 2026.
Your Cordova app can hit that standard if you invest in proper plugin development and server-side handling. The tools are mature enough now that you are not building from scratch.
For a full overview of keeping your app secure beyond biometrics, see top best practices for building secure Cordova applications in 2026.
What You Gain by Going Native
Native biometric integration gives you access to hardware-backed encryption. The fingerprint data never leaves the secure processor on the phone. Your JavaScript code only receives a confirmation token that the biometric matched. This is the gold standard for privacy.
It also improves user trust. When someone sees the system permission dialog asking to use their fingerprint, they know the app is not sneaking data. That trust translates to higher conversion rates and fewer support tickets.
Building for the Next Generation of Devices
By 2026, most midrange phones include under-display fingerprint sensors and 3D facial recognition. Your Cordova app should handle both. The same plugin architecture can support iris scanning and voice recognition as those become standard.
Start with fingerprint and face. Those are the two modalities that users expect and that platform SDKs support reliably.
Your Next Steps
Implementing biometric authentication in your Cordova app is not a weekend project, but it is achievable in a two-week sprint if you follow the path outlined here. Start with a single platform. Get fingerprint working on Android first, then add iOS, then add facial recognition.
Test on real devices from the first day. Emulators cannot simulate a fingerprint sensor.
When you are ready to optimize the rest of your app, look at maximize cross-platform performance in Cordova apps for ways to keep everything running smoothly.
Trust Your Users With the Best Auth
Adding biometrics to your Cordova app is one of the highest-leverage improvements you can make in 2026. Users love it. Security teams approve it. And the technology is finally mature enough that you do not need to be a native mobile developer to pull it off.
Go ahead and wire up that fingerprint sensor. Your users will thank you every time they open your app and get straight to what matters.